


October 7, 2026
October 7, 2026
A banking helpdesk is not a general IT helpdesk with a finance logo on it. It runs inside a regulated perimeter, where a mishandled password reset can become an audit finding. This guide sets out what regulators in Singapore, Malaysia and the European Union expect from your support provider, and which contract terms are mandatory rather than optional.
In short: banking IT helpdesk support is technical support delivered inside a regulated perimeter. Beyond resolving incidents, the provider must satisfy the bank's regulator: contractual audit access, disclosed data location, controlled sub-contracting, tested continuity and a documented exit plan. In Singapore, Malaysia and the European Union these are supervisory obligations, not commercial preferences.
What separates a banking helpdesk from a standard IT helpdesk
Five differences decide whether a support desk is fit for a regulated bank. Each one changes the contract, not just the service description.
The practical consequence is simple. When you evaluate a provider for a bank, you are not only buying response times. You are extending your own compliance perimeter to another company, and you remain accountable for what happens inside it.
Three regulatory frameworks govern most of the banks that ask us this question. If you operate in Singapore, Malaysia or the European Union, at least one of them applies to your support arrangement.
The Monetary Authority of Singapore issued its Guidelines on Outsourcing (Banks), which took effect on 11 December 2024 and apply to all banks and merchant banks in Singapore. They set out board and senior management responsibility for outsourcing risk, due diligence on service providers, protection of data confidentiality and business continuity planning.
A larger change is now in progress. On 6 March 2026 MAS published a consultation paper proposing Guidelines on Third-Party Risk Management, which would supersede the Guidelines on Outsourcing for both banks and non-bank financial institutions. The consultation closed on 20 April 2026. The proposed scope is wider than outsourcing alone: it would cover all financial institutions that rely on third-party services, and it introduces four obligations worth noting now.
The sub-contractor point deserves attention when you outsource a helpdesk. If your provider quietly routes overflow tickets to a fourth party, that is now squarely within scope. Ask where every ticket can physically be seen, not just where the head office is.
Bank Negara Malaysia issued a Policy Document on Outsourcing that took effect on 1 January 2019 and applies to licensed banks, investment banks, Islamic banks, insurers, takaful operators and development financial institutions. Its requirements run along similar lines: board accountability, due diligence on the provider's capability and location, contractual regulator access, data confidentiality, business continuity and a defined exit strategy.
The Digital Operational Resilience Act has applied since 17 January 2025. It covers financial entities operating in the EU and their critical ICT third-party service providers, including providers based outside the EU. Among its requirements, financial entities must keep a complete and current register of all contracts with third-party ICT providers.
That last clause matters for any Asian provider serving a European bank, and for any European bank running support out of Asia. A provider that has already been inside a DORA register knows what evidence a supervisor asks for. One that has not will be learning on your engagement.
Reading the three frameworks side by side, the overlapping demands are consistent. Use this as the compliance section of your request for proposal.
None of these are unusual requests. A provider that has served regulated clients will have the answers ready. Hesitation on audit access or delivery location is the clearest early warning you will get.
Most banks already know the general L1 to L3 model, and we have covered that structure in detail in our guide to IT support levels. What changes in banking is not the number of tiers but what sits inside each one.
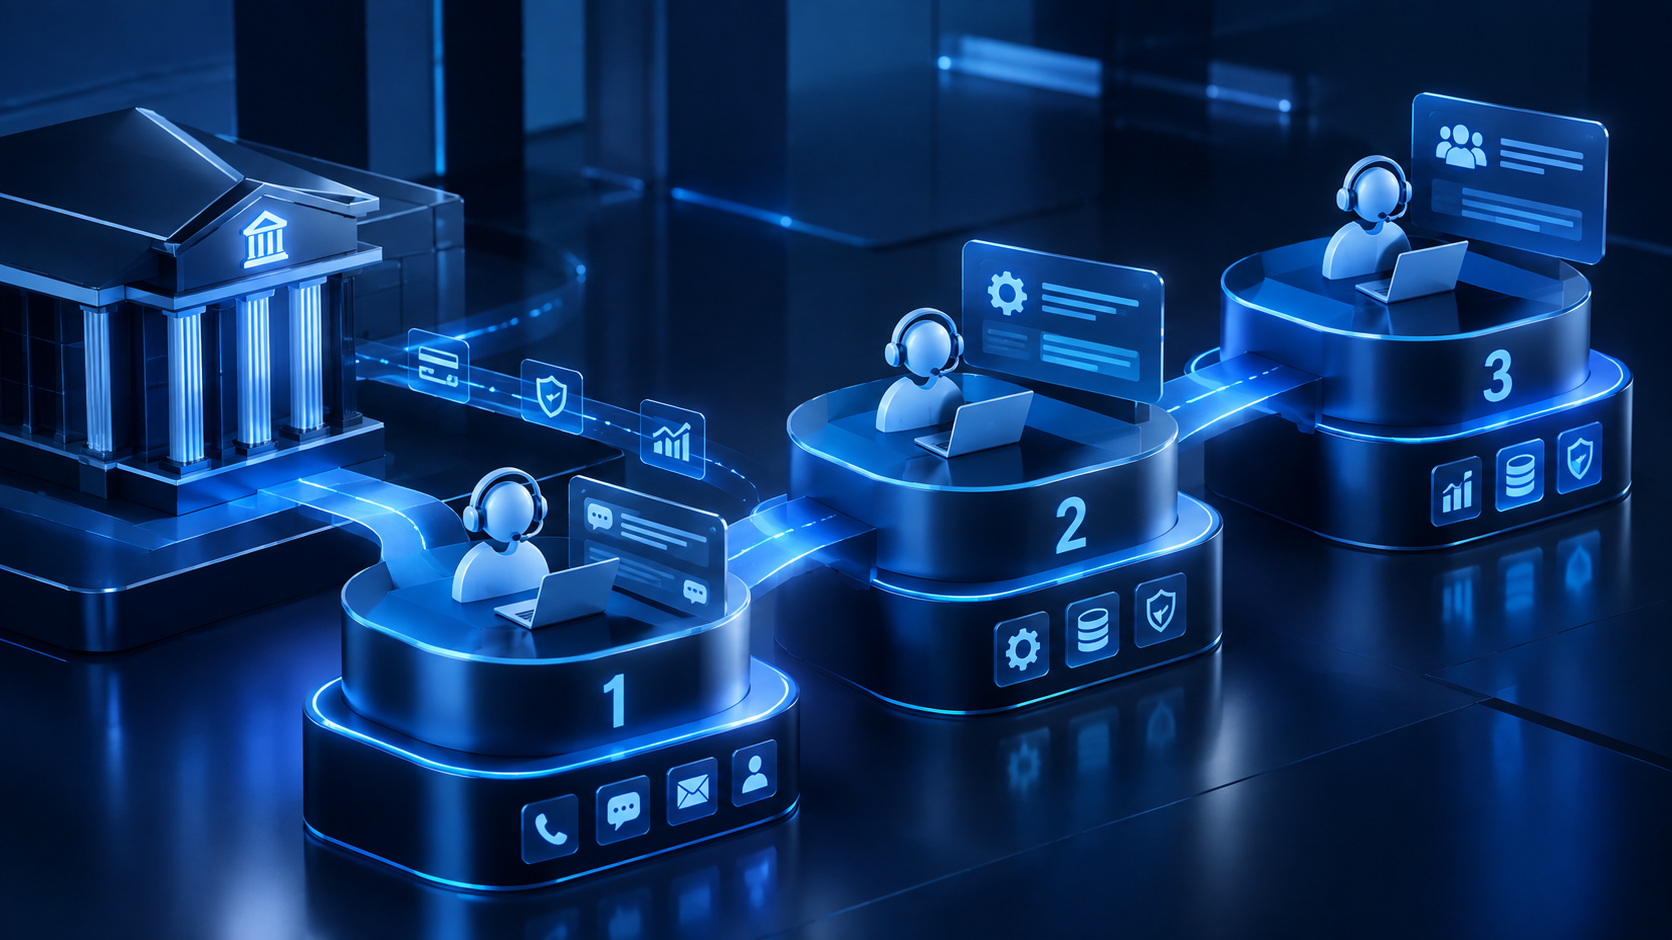
At tier 1, the volume driver in a bank is rarely a broken laptop. It is access. Branch staff locked out of the teller application between opening and the first customer, a relationship manager whose token has expired, a new joiner who needs entitlements across four systems. These are fast tickets with a compliance tail, because every identity action leaves an audit trail someone will eventually read.
Tier 2 is where banking specificity begins. The agent needs to know the difference between a payment file that failed validation and one that failed transmission, because the first is a business problem and the second is an incident. Generic technical support cannot make that distinction, which is why a banking desk needs runbooks written against your actual systems.
Tier 3 touches core banking platforms, payment rails and the integration layer between them. Many banks keep this in house permanently, and that is a defensible choice. The productive outsourcing boundary usually sits between tier 2 and tier 3.
A service level agreement written for a general business will not survive an operational resilience review. The correction is to define priority by banking impact rather than by ticket type.
Treat these as a drafting starting point and calibrate them to your own cut-off times, since a payment cut-off at 16:00 makes an 8 hour resolution target meaningless for a batch failure discovered at 15:00.
Three further clauses are worth insisting on. First, define the measurement window and who reports it, because a provider reporting on its own performance without raw data is not measurable. Second, set service credits that are large enough to change behaviour. Third, agree what happens on repeated breach, since credits alone never fixed a structurally under-resourced desk.
Be careful with the headline availability number. A vendor offering 99.999 percent uptime is offering roughly five minutes of unplanned downtime per year across the whole service. Ask what that figure is measured against and whether planned maintenance is excluded, because the exclusions usually matter more than the number.
Banking support has to cover the hours your systems run, which for payment and card systems means continuously. There are three workable models.
A single offshore desk with shift rotation is the simplest to manage and the cheapest to run, though night shifts tend to carry weaker staff retention. A follow-the-sun model across two or three regions gives every ticket a daytime team, at the cost of handover discipline and a higher price. A hybrid keeps tier 1 offshore around the clock while tier 2 and tier 3 work business hours in a zone close to the bank, which suits most mid-sized institutions.
Time zone overlap is the variable that most buyers underestimate. Vietnam sits exactly one hour behind Singapore, so a Vietnam-based team shares a full working day with a Singapore bank. Escalations get resolved in the same shift rather than the next one. Compared with a Central or Eastern European desk, where the usable overlap with Singapore is a narrow window at the edge of both working days, the operational difference shows up in tier 2 resolution times rather than in the contract.
Every framework above requires the bank to know where its data lives and who can reach it. For a helpdesk that means four concrete questions.
Where is the ticketing system hosted, and is that jurisdiction acceptable to your regulator? What customer data actually enters a ticket, and can you reduce it? Screenshots attached to tickets are the most common leak of production customer data into a support system, and masking them at source is easier than governing them afterwards. Who at the provider can read a ticket, and is that access logged and reviewable by you? What happens at the end of the contract, and in what format does your data come back?
Vietnam has become a credible answer to these questions for banks in the region, and we examined why in our analysis of data security in outsourcing. Where support work touches privileged access or security tooling, it belongs alongside a defined security management scope rather than inside a general support contract.
Score each item as evidenced, claimed or absent. Anything that stays at "claimed" after two conversations should be treated as absent.
The final item is easy to verify and frequently decides the engagement. Ask for the working hours of the specific team that would serve you, not the company's global coverage statement.
Can a bank outsource its helpdesk at all under MAS rules?
Yes. Neither the Guidelines on Outsourcing (Banks) nor the proposed Third-Party Risk Management Guidelines prohibit outsourcing. They require the bank to govern the arrangement, evaluate the risk and retain accountability. Outsourcing the work does not outsource the responsibility.
Does the MAS third-party risk consultation change anything today?
The consultation closed on 20 April 2026 and the final guidelines were not yet in force at the time of writing. Because the proposed scope is wider than the current outsourcing guidelines, it is worth checking the current status on the MAS website before signing a multi-year support contract, and building a third-party register now if you do not already keep one.
Should tier 3 support be outsourced?
Usually not in the first engagement. Tier 3 touches core banking and payment systems where institutional knowledge carries most of the value. A common path is to outsource tier 1 and tier 2, measure for two or three quarters, then decide.
How long does transition take?
For a mid-sized bank, plan for eight to twelve weeks covering knowledge capture, runbook writing, shadowing and a phased cutover. Compressing this below eight weeks is the most reliable way to produce a bad first quarter.
Conclusion
The decision in front of most banks is not whether to outsource support, but whether a given provider can operate inside a regulated perimeter without creating findings. That question is answered by evidence, and the checklist above is the fastest route to it.
Serdao has run technical support and software delivery for eighteen years from a French head office with production in Ho Chi Minh City, a structure that puts European governance practice and Southeast Asian working hours in the same engagement. We are members of CCI France Vietnam and la French Tech. If you want to see how this maps to your environment, our helpdesk support and technical support pages set out the scope in detail, and you can contact our team to discuss your requirements.